

 fa02ff2d26
* feat(executable): capture GNU ELF build IDs

Capture GNU ELF build IDs in Syft JSON so consumers can correlate
otherwise unidentified binaries with known artifacts or build records.

Read GNU build-ID notes from .note.gnu.build-id, with a 64 KiB read limit.
Validate the note owner and type before recording the identifier.

Add focused extraction and JSON round-trip tests and update the schema.

Signed-off-by: Mario Corchero <mcorcherojim@bloomberg.net>

* chore: bump JSON schema to 16.1.13 for executable identifiers

16.1.12 landed on main for coordinate fullPath, so the identifiers
addition moves to the next version.

Signed-off-by: Alex Goodman <wagoodman@users.noreply.github.com>

* feat(executable): capture go build IDs from .note.go.buildid

The go linker only writes a GNU build ID with -B or when linking
externally, so most pure-Go binaries had no identifier. Every go ELF
carries .note.go.buildid, captured as kind `go-build-id` in the form
`go tool buildid` prints.

Signed-off-by: Alex Goodman <wagoodman@users.noreply.github.com>

* docs(executable): describe identifiers generically

Identifier field docs (and the published schema) now give GNU hex and
Go build IDs as examples instead of stating every value is a GNU build
ID in lowercase hex, so the contract holds as more kinds are added.

Signed-off-by: Alex Goodman <wagoodman@users.noreply.github.com>

* fix(executable): keep identifier notes inside elfutil bounds

Register `.note.gnu.build-id` and `.note.go.buildid` in elfutil's
sectionsReadByName as that list asks, and never open a compressed
identifier note. Real ones are SHF_ALLOC and cannot be compressed, so
this drops the only decompression path into these reads.

Signed-off-by: Alex Goodman <wagoodman@users.noreply.github.com>

* test(executable): check identifiers from real linker output

Cross-compiles a tiny go program with `-B` so the test sees a GNU
build ID and a go build ID written by an actual linker and read through
the cataloger entrypoint.

Signed-off-by: Alex Goodman <wagoodman@users.noreply.github.com>

---------

Signed-off-by: Mario Corchero <mcorcherojim@bloomberg.net>
Signed-off-by: Alex Goodman <wagoodman@users.noreply.github.com>
Co-authored-by: Mario Corchero <mcorcherojim@bloomberg.net>
Co-authored-by: Alex Goodman <wagoodman@users.noreply.github.com>

Syft
A CLI tool and Go library for generating a Software Bill of Materials (SBOM) from container images and filesystems. Exceptional for vulnerability detection when used with a scanner like Grype.



Features
- Generates SBOMs for container images, filesystems, archives (see the docs for a full list of supported scan targets)
- Supports dozens of packaging ecosystems (e.g. Alpine (apk), Debian (dpkg), RPM, Go, Python, Java, JavaScript, Ruby, Rust, PHP, .NET, and many more)
- Supports OCI, Docker, Singularity, and more image formats
- Works seamlessly with Grype for vulnerability scanning
- Multiple output formats (CycloneDX, SPDX, Syft JSON, and more) including the ability to convert between SBOM formats
- Create signed SBOM attestations using the in-toto specification
Tip
New to Syft? Check out the Getting Started guide for a walkthrough!
Installation
The quickest way to get up and going:
curl -sSfL https://get.anchore.io/syft | sudo sh -s -- -b /usr/local/bin
Tip
See Installation docs for more ways to get Syft, including Homebrew, Docker, Scoop, Chocolatey, Nix, and more!
The basics
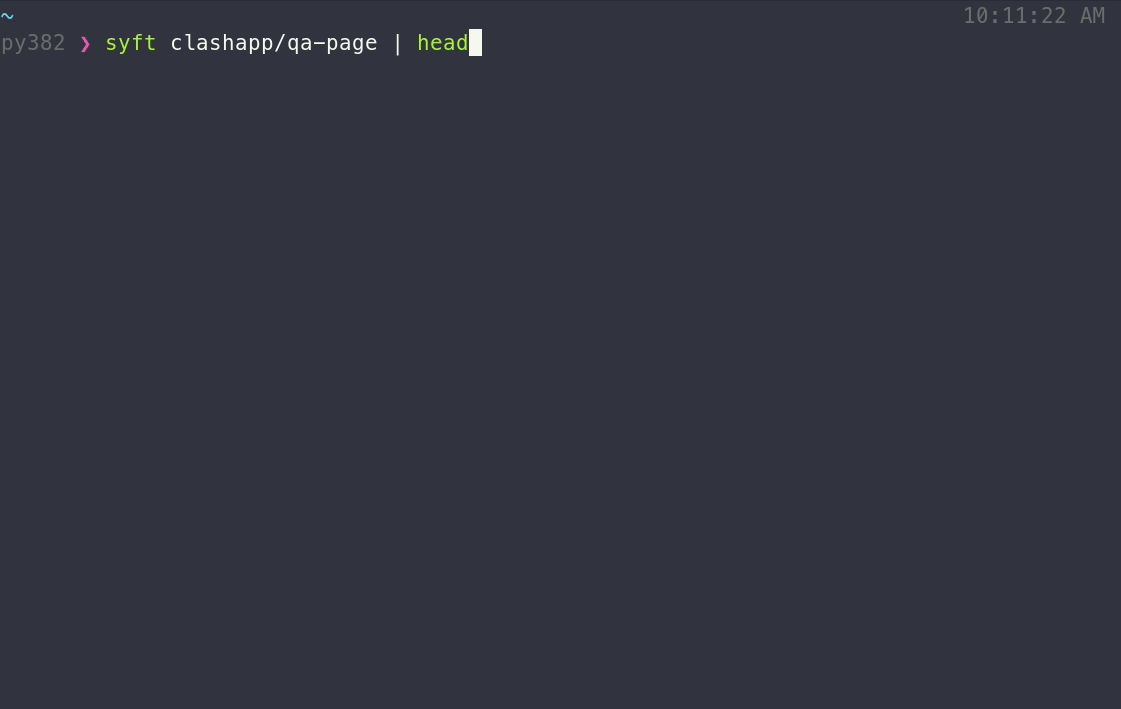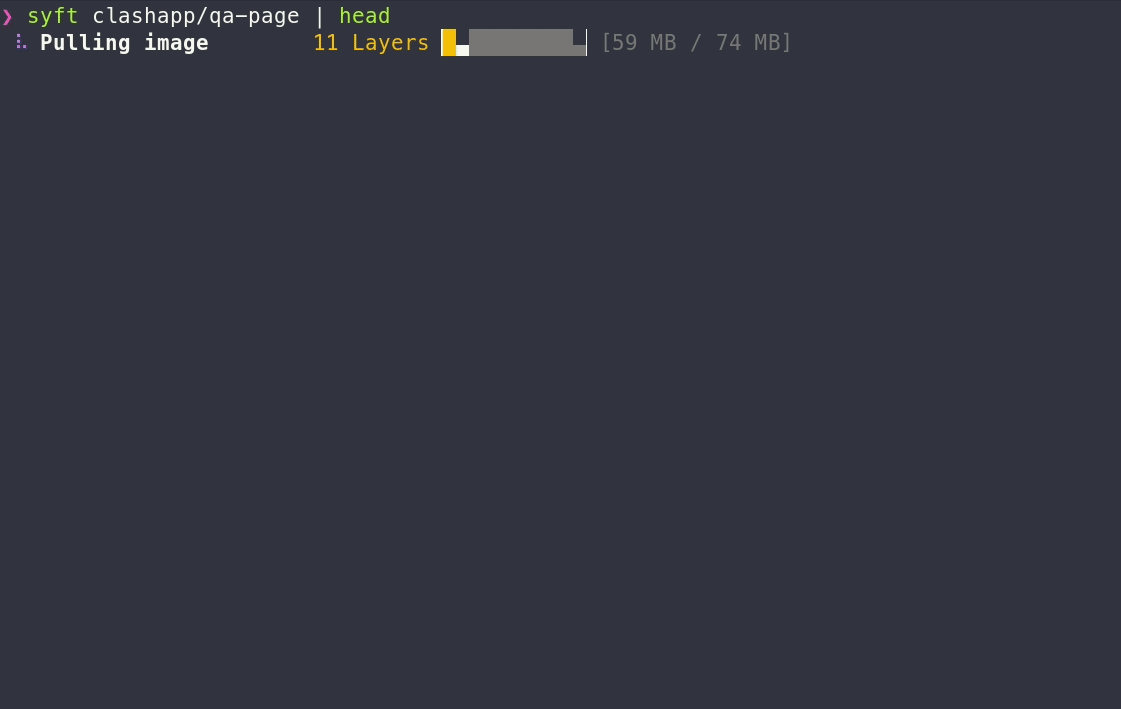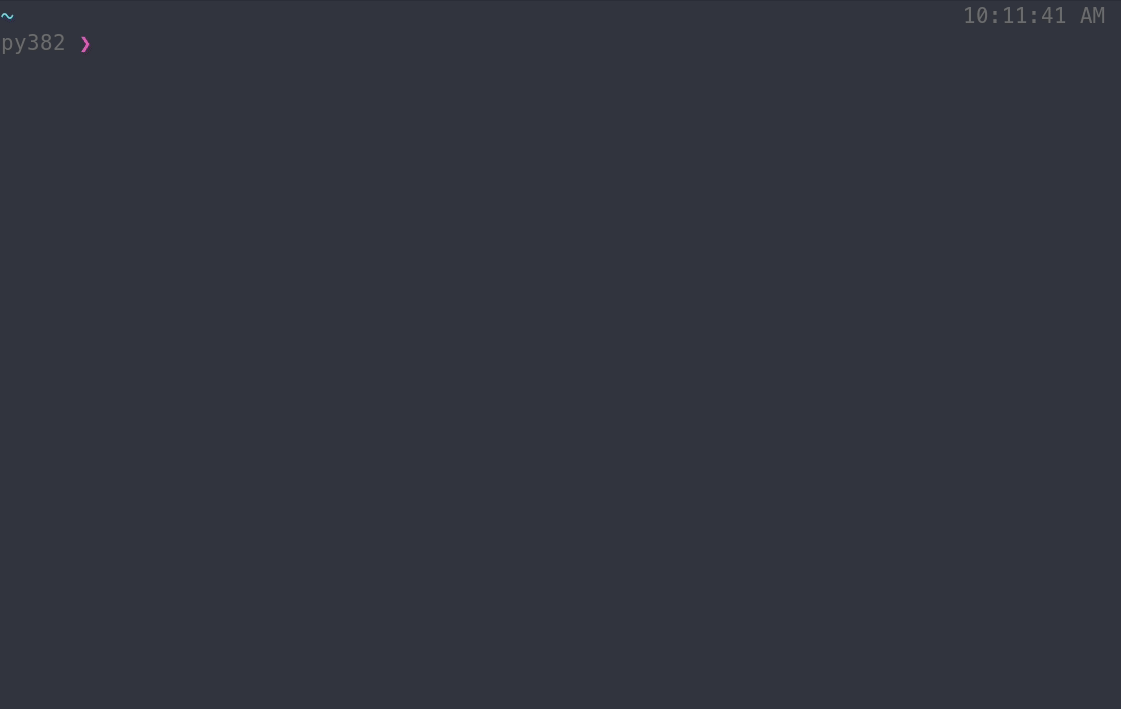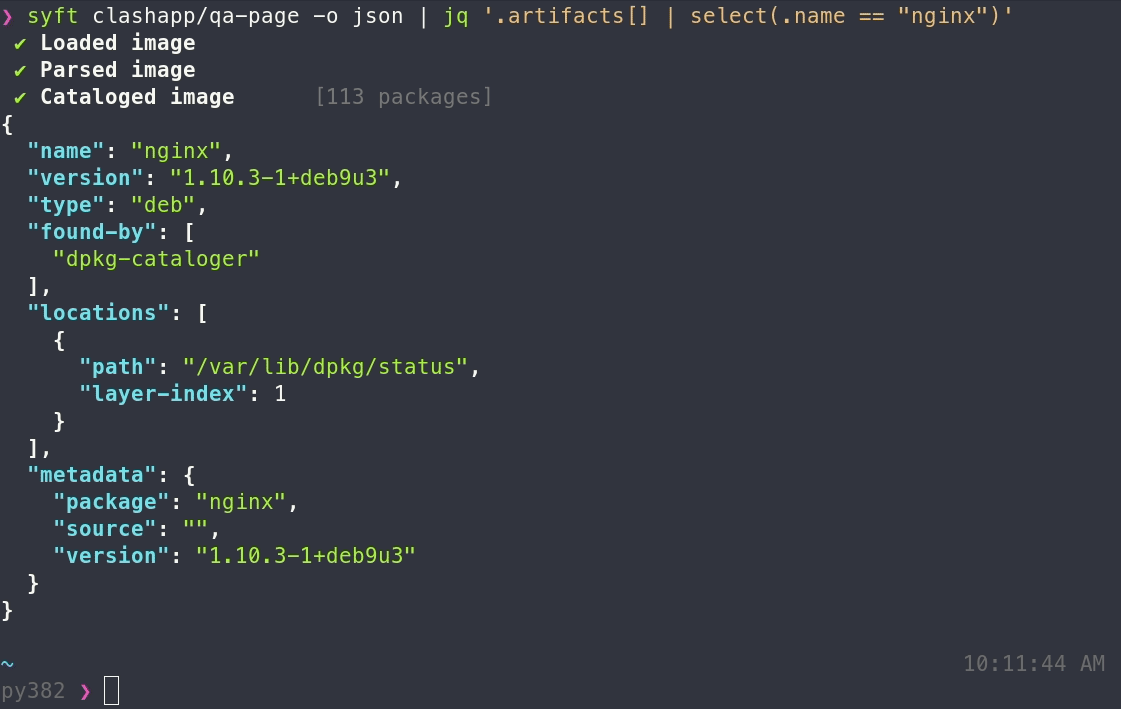
See the packages within a container image or directory:
# container image
syft alpine:latest

# directory
syft ./my-project
To get an SBOM, specify one or more output formats:
# SBOM to stdout
syft <image> -o cyclonedx-json

# Multiple SBOMs to files
syft <image> -o spdx-json=./spdx.json -o cyclonedx-json=./cdx.json
Local containers-storage images
On Linux, syft can scan images from a local containers-storage store (e.g. built with Buildah or Podman) when asked explicitly; plain image references never look there:
syft --from containers-storage localhost/myimage:latest

# rootless stores must be read from inside the builder's user namespace
podman unshare syft --from containers-storage localhost/myimage:latest
This is included in the Linux release binaries. When building from source, add -tags containers_image_openpgp,exclude_graphdriver_btrfs.
Tip
Check out the Getting Started guide to explore all of the capabilities and features.
Want to know all of the ins-and-outs of Syft? Check out the CLI docs, configuration docs, and JSON schema.
Contributing
We encourage users to help make these tools better by submitting issues when you find a bug or want a new feature. Check out our contributing overview and developer-specific documentation if you are interested in providing code contributions.
Syft development is sponsored by Anchore, and is released under the Apache-2.0 License.
The Syft logo by Anchore is licensed under CC BY 4.0


For commercial support options with Syft or Grype, please contact Anchore.
Come talk to us!
The Syft Team holds regular community meetings online. All are welcome to join to bring topics for discussion.
- Check the calendar for the next meeting date.
- Add items to the agenda (join this group for write access to the agenda)
- See you there!